


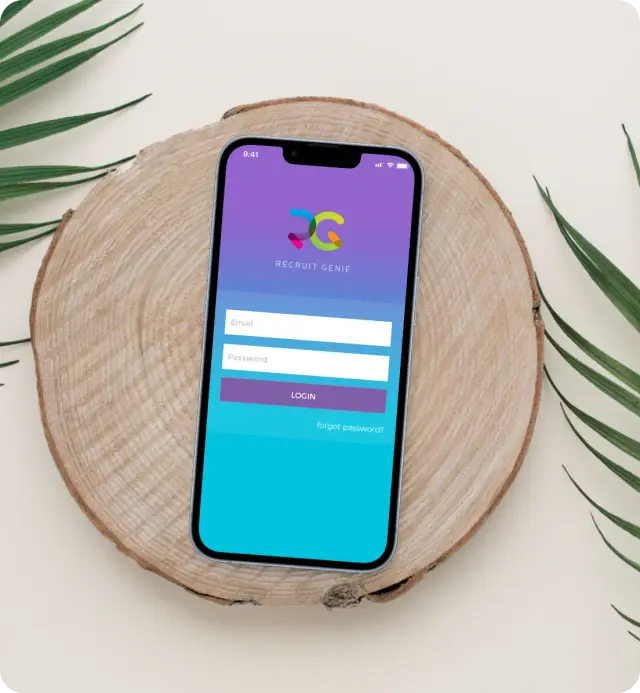
Recruit Genie
An HR platform with identity checks, role-based access and training schedules, for a UK client.
Before strangers sign up and pay, find out what they could see. We test your app the way someone with bad intentions would, and give you a plain report of what to fix first.
AI tools write code that works for the person testing it. Security problems show up when a different person uses it. That person might change an ID in a request, call an API without logging in, or read a key out of the browser. In 2025, one public report found 170+ apps built with a popular AI builder that let anyone read data from their databases. None of those apps looked broken.
Built with Lovable and Supabase? See Lovable and Supabase apps for what we usually find there.
| Test | In plain words |
|---|---|
| Cross-user access | We log in as user A and try to read and change user B’s data, through the app and directly against the API and database. |
| Database rules | Every table’s access policy (Supabase RLS or your own checks), tested, not just read. |
| Authentication | Sign-up, login, logout, reset, session expiry, social login. Does logout really log you out? |
| Exposed secrets | Keys in the frontend bundle, the repo, and the git history. |
| Server routes | Which endpoints work without login, or with the wrong role. |
| Payments | Webhook signature checks, refund and failure paths, and whether paid access can be granted without paying. |
| File uploads | Who can read uploaded files, and whether file links are guessable. |
| Basics | HTTPS, security headers, rate limits on login and forms, error messages that leak details. |
Scanners are good at known patterns, and we use them too. They can't know that a coach should see their own clients and not another coach's. Rules like that are where the serious leaks are, and they need a person to test them.
$490, 3 working days from access. Same audit as the first step of Ship It, so if you also want the app in the stores, we check store readiness at the same time.
Web app only, no app store? The same audit covers it, and we skip the store checks. If you want us to fix what we find, the sprint for a web app covers sign-in, payments, hosting, speed and security instead of store submission, at a fixed price we give you with the report.
Not sure yet? Run through the free 15-point check first. Items 6 to 10 are security checks you can do yourself.
“We brought iMobile Designs in to improve and refine an existing web application, and they handled everything efficiently. Communication was clear, turnaround was fast, and the final implementation was exactly what we needed.”